




How Insignia Financial’s CISO tackles emerging threats and open-source risks
James Ng, GM Cyber Security (CISO) at Insignia Financial, shares how the company tackles emerging threats, open-source risks, and strengthens governance and identity management in this Security Edge interview.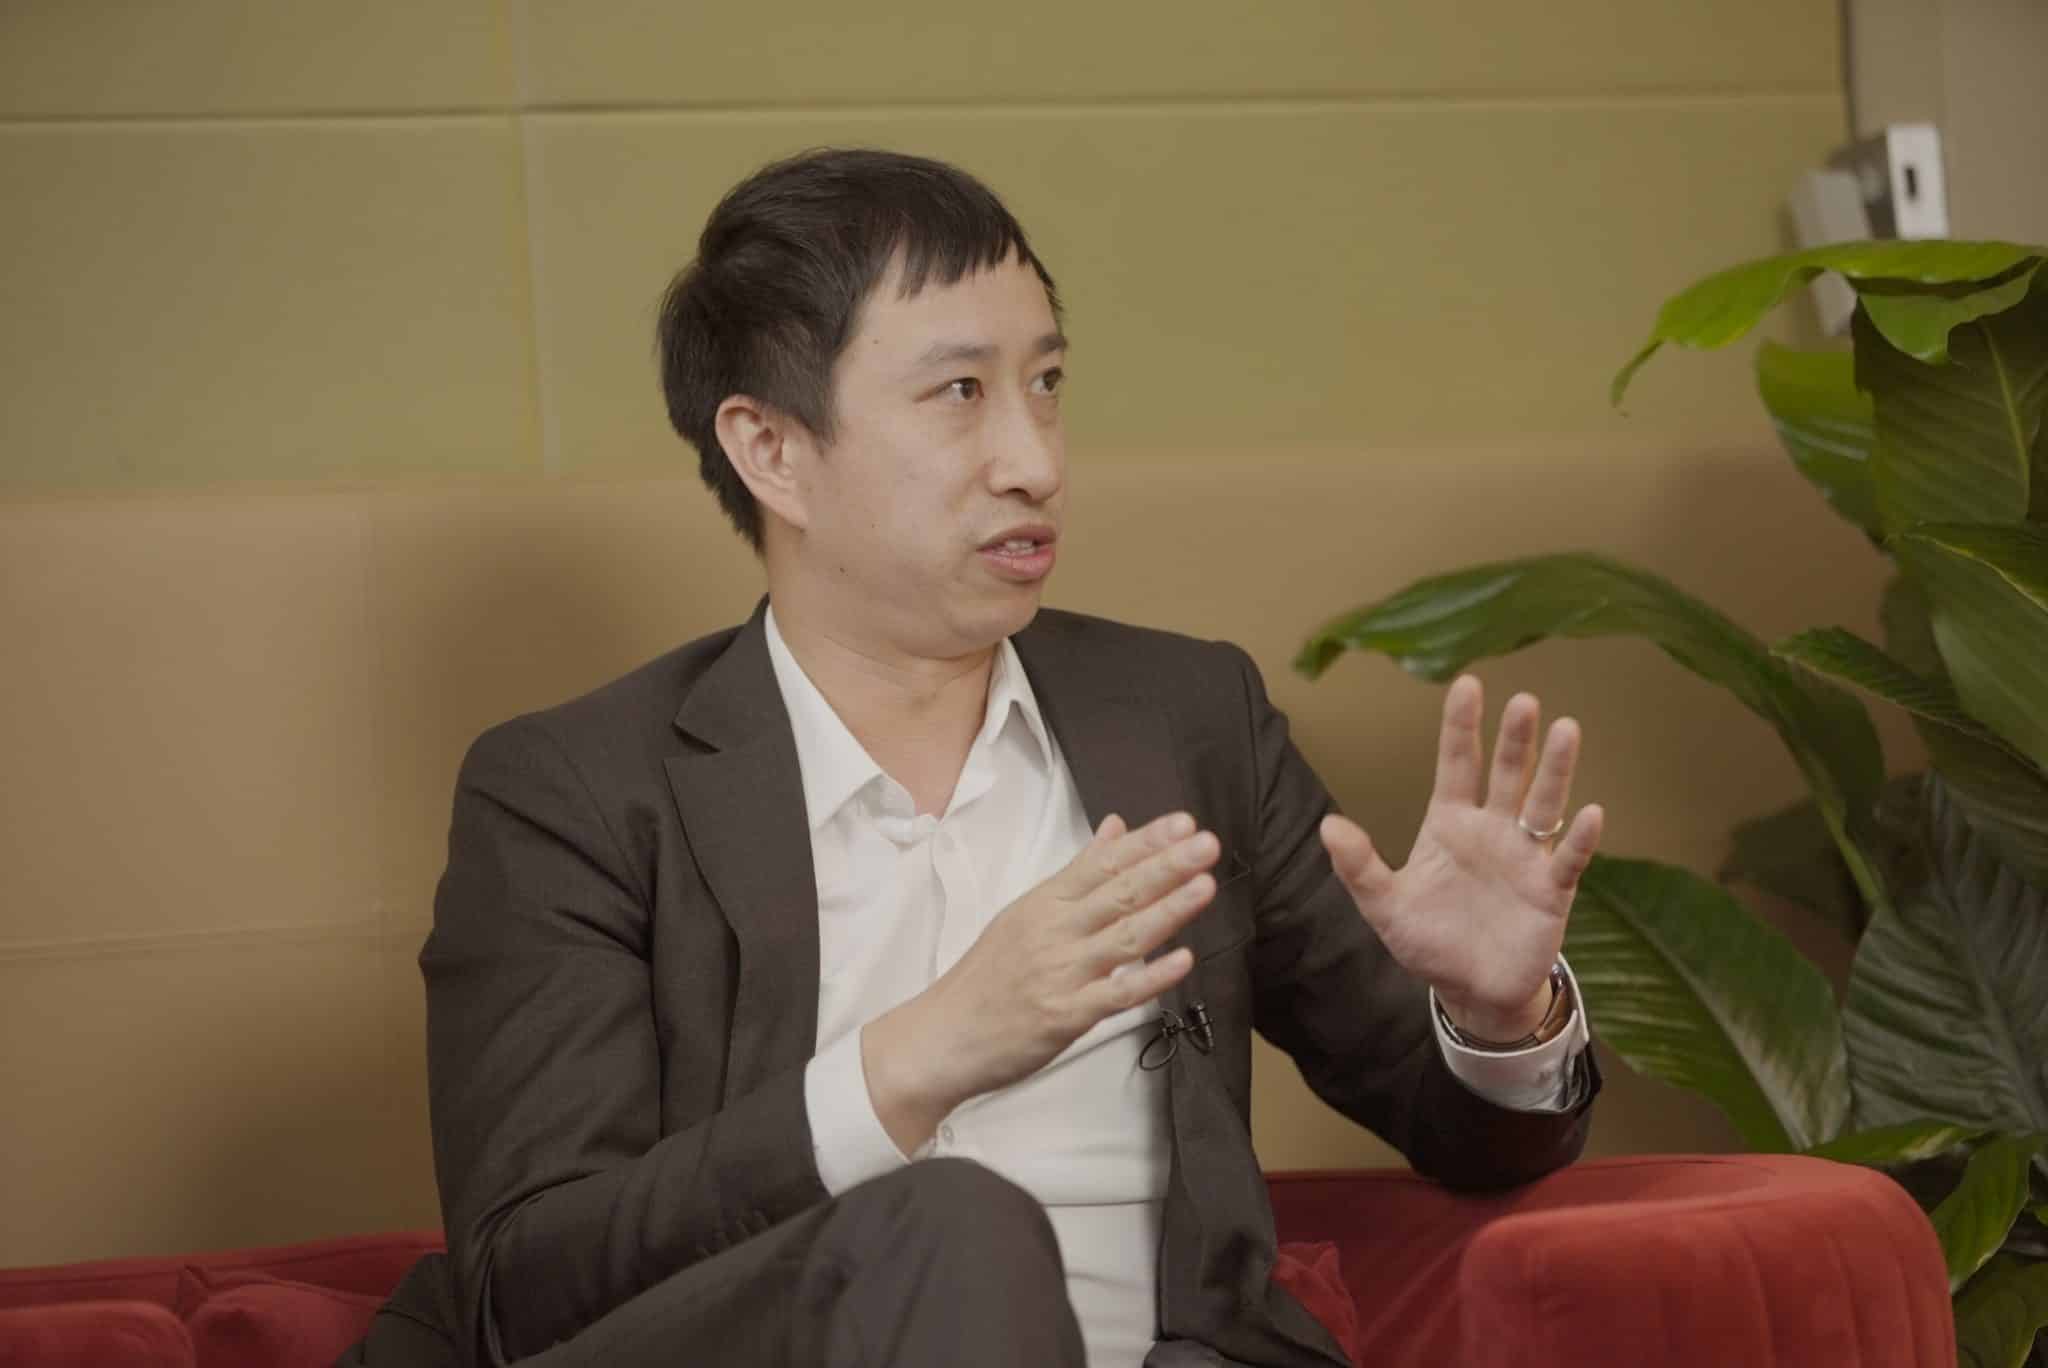


 Published Nov 4, 2024 in
Peer Insights
Security
Contributors
James Ng
Byron Connolly
Wealth management organisation, Insignia Financial, is prioritising its cyber security investments to protect the retirement savings and personal data of its two million customers.
CISO James Ng who joined Insignia in October 2023, discovered that the ASX200 company had inherited “different processes and ways of doing things” through recent acquisitions. This arose as banks moved away from the wealth management sector.
In 2021, the transition of MLC Wealth from NAB to Insignia Financial was one of the largest wealth management separations in Australia. In October 2022, Insignia completed the separation of the pensions and investments business from ANZ Bank. More than 1,200 staff moved from ANZ to Insignia.
Ng told ADAPT that Insignia’s multiple Boards have shown strong interest in cyber security risks. This ‘top-down’ approach has guided the organisation’s efforts to improve its cyber maturity.
He says Insignia used the NIST Cyber Security Framework to assess its security domains and map existing skillsets, identifying gaps in its capabilities.
“We aligned with NIST domains, we did the mapping with our current talent and then looked at where we needed to grow and invest to set us up for success. That revolved around putting together a business case, a model and then [giving it to] the executive and Boards for approval,” he says.
The organisation also engaged two independent specialists in addition to its CP 234 audits, to comply with the Australian Prudential Regulation Authority (APRA) standards ensuring regulated entities like Insignia maintain robust information security measures.
“A lot of our focus is understandably about maturing our processes. This [audit] very much looked at how do we strengthen our third-party security governance activities? How do we strengthen our identity and privileged access management controls as well?
“So, through the maturity assessment, when we looked at controls like identity and PAM (privileged access management), we’ve got an opportunity to roll out something a bit more consistent across the estate,” says Ng.
ADAPT has found that cyber threats and strict regulatory standards are compelling FSIs to prioritise cyber security investments.
A July 2023 cyber security review by APRA highlighted gaps in how many financial institutions manage cyber and information security risks.
Common issues include:
- the failure to identify critical and sensitive information assets
- inadequate testing of control programs
- outdated incident response plans
- limited assessment of third-party information security capabilities.
Threat education and learnings
Phishing and business email compromise attacks via social engineering – as well as quishing, a type of phishing attack that uses QR codes – are very common at the moment.
Ng says gone are the days of simple ‘Prince of Nigeria’ email-based social engineering attacks. Cyber crooks tap into the social conscience with new, more novel ways to bypass security controls using malicious links and attachments in emails.
He says Insignia is typically seeing quishing and more advanced business email compromise attacks that are used to establish rapport between an individual and a target. These attacks don’t necessarily include anything malicious up front, but over time, bad actors will coax someone to go to a website and provide detailed information.
“A key thing for us at Insignia Financial is, ‘how do we make it real for our people? So, in our training modules and engagement exercises – we use examples that we have observed in then organisation to make it real for [staff] and bring it all close to home,” he says.
Insignia’s clients regularly reach out to its financial advisors who are seeking information or requesting support. Insignia has seen a lot of instances where threat actors have been impersonating clients in an effort to elicit information through social engineering.
“They’re the indirect methods because we often say, ‘don’t click on [messages] from untrusted individuals.’ In this instance, there is often a trusted relationship between the advisor and the client,” he says.
Insignia reports cyber threats and updates to its Boards and sub-committees quarterly. They are also provided with “out of cycle” briefings when regulatory changes are made such as the recent introduction of Australia’s first Cyber Security Act 2024, which became law in November.
These meetings are supplemented with ‘lunch and learn’ sessions where Boards are provided with updates on the changing threat landscape and ‘deep dives’ into areas of interest.
One of these areas is Insignia’s cyber incident response plans and their integration with the organisation’s crisis management processes, including the roles Boards play during incidents.
 James Ng
GM Cyber Security (CISO) at Insignia Financial
A leader with a range of experience across various cyber security, technology risk and audit domains. Motivated to create and maintain high performing cultures in order to drive business focused outcomes collaboratively with stakeholders.
Worked internationally across Australia, USA, Hong Kong, Thailand, Philippines, Singapore, India, Papua New Guinea and the UK (IOM).
Currently a:
– Graduate of the Australian Institute of Company Directors (GAICD),
– GIAC Security Operations Manager (GSOM – SANS),
– Certified Information Systems Security Professional (CISSP – ISC2),
– Certified Information Systems Auditor (CISA – ISACA),
– Certified Associate in Project Management, now lapsed (CAPM – PMBOK/PMI), and
– Certified Professional in Cloud Security (CCSK – Cloud Security Alliance)
 Byron Connolly
Head of Programs & Value Engagement at ADAPT
Byron is a highly experienced technology and business journalist, editor, corporate writer, and event producer.
Prior to joining ADAPT, he was the editor-in-chief at CIO Australia and associate editor at CSO Australia. He also created and led the well-known CIO50 awards program in Australia and The CIO Show podcast.
Byron creates valuable insights for our community of senior technology and business professionals that help them reach their organisational and professional goals. He has a passion for uncovering stories about the careers and personal philosophies of Australia’s top technology and digital executives.
When he is not working, Byron enjoys hot yoga, swimming, running and spending time with his family. He completed the North Face 100km ultra marathon in the NSW Blue Mountains in 2012 and 2013.
Less Join the ADAPT
Insider Community
Get the latest A/NZ market research and insights on the core trends impacting leaders.
Join the ADAPT Insider Community
Get the latest A/NZ market research and insights on the core trends impacting leaders.